Please, briefly introduce yourselves and describe your role in the development of the secure element.
Augusto Wankler Hoppe: I am the technical lead and architect of the secure element chip at Fraunhofer IIS. I am responsible for the entire technical implementation, from architectural design through physical implementation to silicon validation. I oversee the collaboration between design, manufacturing, and business development.
Andreas Seelos-Zankl: I am a Principal Scientist at Fraunhofer AISEC and am responsible for coordinating the security aspects of our secure element. This includes, for example, supporting post-quantum cryptography and ensuring system integrity. In the early stages, I was also responsible for coordinating the Trusted Electronic Bayern Center (TrEB), the overarching project from which the secure element emerged.
How large are the teams involved in the secure element at Fraunhofer IIS and AISEC?
Andreas Seelos-Zankl: At the peak of the project, up to ten researchers were working on security and cryptography; I coordinated their work and aligned it with our steering committees.
Augusto Wankler Hoppe: On our side, at least 15 people were involved in the project’s development. We had various teams working on this, for example, on design verification.
What gaps or weaknesses in existing secure element or TPM (Trusted Platform Module) solutions motivated you to develop your own chip?
Andreas Seelos-Zankl: Here at Fraunhofer AISEC, analyzing and testing microcontrollers and security chips has been part of our daily routine for many years. In doing so, we’ve observed that secure element solutions have generally been either very secure but expensive, or very inexpensive but too insecure. Expensive systems are used only in a few specialized areas, while the inexpensive ones, although widely used, remain easily vulnerable due to their lack of protective measures. This is precisely the gap we wanted to close. That’s why we’ve long wanted to develop a microcontroller platform that offers a high level of security while also being flexible and easy to use, allowing for broad adoption. At the same time, the hardware sector – which had previously been difficult to access – has opened up significantly in recent years: More and more designs, tools, and complete system-on-chip (SoC) architectures have become available as open source, and this trend has finally reached security chips as well. The key catalysts for us were the OpenTitan project, which aims to create precisely such a security chip with a high level of security, and the simultaneous launch of the Bavarian initiative to promote microelectronics, which was a perfect fit. Together with our colleagues from Fraunhofer EMFT and, in particular, from Fraunhofer IIS, who joined the project, the way was clear to actively advance this topic together.
Augusto Wankler Hoppe: From a chip architecture perspective, another point was crucial for us at Fraunhofer IIS: the open-source nature significantly increases transparency. OpenTitan, the project which our secure element is based on, has been extensively tested and analyzed by many partners, so we are building on a very secure foundation. From an architectural standpoint, the connection to a secure element is a key vulnerability, especially in the case of discrete components mounted on the circuit board as separate modules. That is why we decided to develop a secure element that is not just a discrete component, but a solution that can be embedded directly into a SoC. While similar solutions exist today, we were involved in this development early on and placed great emphasis on compatibility from the very beginning. That is why we based our approach on Caliptra, an industry standard for data center security defined by an industry consortium, which systems integrated into data centers will be required to comply with in the future. In addition, we are in constant dialogue with the industry to understand the direction in which the market is moving and to further develop our solution accordingly.
For which application scenarios is the secure element primarily designed?
Augusto Wankler Hoppe: These days, most products need a trust anchor within the system. For example, we need to be able to trust that our cars cannot be tampered with by anyone. The secure element serves as this trust anchor and is, in that sense, universally adaptable. But we also have specific markets that we’re particularly targeting.
Andreas Seelos-Zankl: The project we’re building on was originally developed for integrity protection and authentication; for example, to secure IT infrastructure. Beyond that, however, our secure element is also relevant for many other areas, from the Internet of Things and smart factories to medical technology, the automotive industry, payments, and critical infrastructure. Thanks to our regional manufacturing capabilities, the defense sector also plays a role, as it allows us to better ensure technological sovereignty. The only current limitations are applications that require specific certifications or very specific standards; an additional step is still needed here, as we have not yet tailored the secure element to individual markets. In principle, however, it can be used in all of these markets.
What does the general architecture of the secure element look like, and how does it differ from comparable solutions?
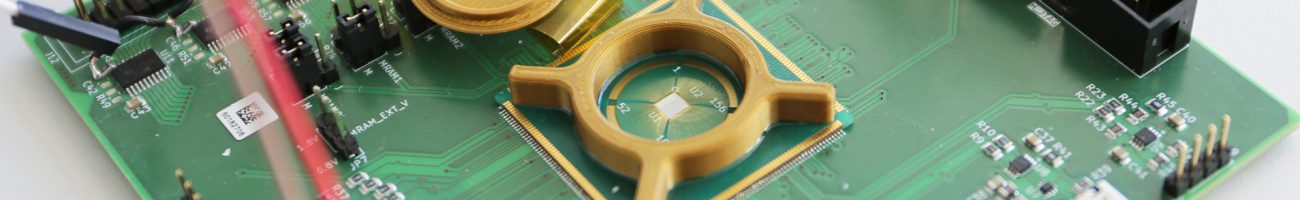
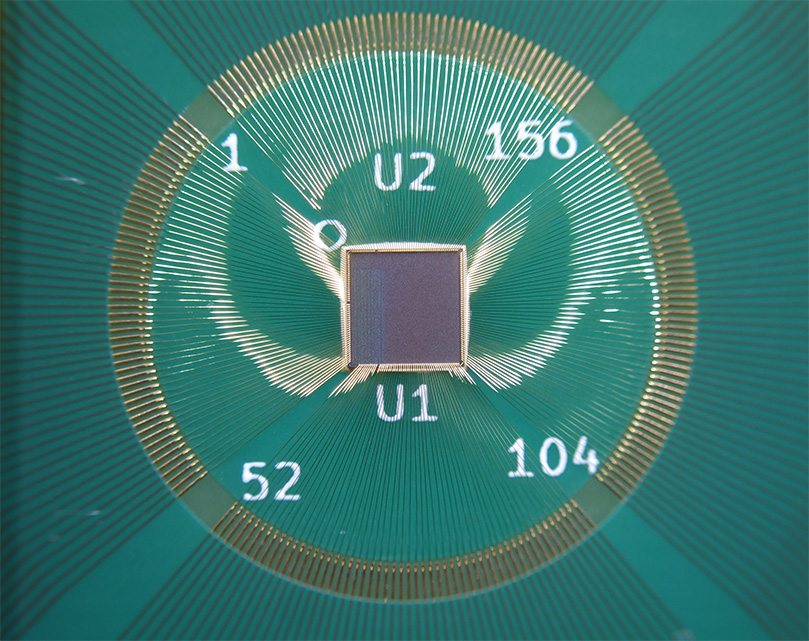
Augusto Wankler Hoppe: We at Fraunhofer IIS are responsible for the architecture and physical implementation of the secure element. Our secure element is based on the open-source project OpenTitan. We have further developed it and expanded it to include a Caliptra-based communication interface that we developed ourselves. This interface enables secure communication with application processors and other components of a SoC. We have modified OpenTitan so that it functions not only as general-purpose soft IP but also as a specific implementation for GlobalFoundries’ 22FDX technology. This means we have adapted OpenTitan so that it is no longer just a “general blueprint” for security hardware, but is specifically tailored to a particular chip manufacturing technology from GlobalFoundries, allowing it to be implemented directly and efficiently as part of an actual chip. We also incorporate physical security mechanisms. We have integrated secure, non-volatile (i.e. permanent) memory such as eFuses and eMRAM; initial silicon validations have already been successfully completed.
Andreas Seelos-Zankl: On the one hand, our system can be used as a standalone microcontroller, like many traditional secure elements. But on the other hand, it can also be integrated into SoC platforms. In doing so, we have placed great emphasis on flexibility: Instead of committing to a single standard, we support various specifications such as TPM and Caliptra. Technologically, we rely on a modern 22-nanometer process from GlobalFoundries, whereas many secure elements today are still manufactured using larger process technologies. This represents a significant step forward for us while allowing us to remain regionally based, as chip manufacturing takes place in Dresden, Germany. Another key difference is our early support for post-quantum cryptography (PQC): We already offer hardware that covers a wide range of modern PQC algorithms.
Which of the essential security requirements defined in the Cyber Resilience Act do you explicitly address with this secure element architecture, and how is that reflected in the design?
Andreas Seelos-Zankl: Among other things, the Cyber Resilience Act defines catalogs of security requirements and vulnerability management, many of which we directly address with our secure element technology, such as data confidentiality and integrity, the reduction of attack surfaces, and protection against unauthorized access. All of these are reflected in the overall system design. The provision of security updates is also part of our approach, although structured processes are, of course, still necessary to roll out these updates regularly and reliably.
Augusto Wankler Hoppe: At the implementation level, CRA compliance means that our secure element provides technical security functions that address typical attack and application scenarios. In this way, our secure element helps protect our customers’ assets as well as their intellectual property. In addition, we support our customers in establishing and implementing a Secure Development Lifecycle (SDL). So we don’t just offer a ready-made “plug-and-play” solution; we also support our customers in reviewing, refining, and addressing their security requirements with regard to the secure element. This enables us to provide customer-specific solutions.
Against which attack models is your secure element designed (e.g., remote at-tacks, physical access, side-channel attacks), and what key hardware protection mechanisms do you employ?
Augusto Wankler Hoppe: Our secure element was designed based on specific threat models. In doing so, we primarily followed guidelines that comply with Common Criteria certifications, particularly the protection profiles for secure elements; not only for discrete, i.e., standalone secure elements such as Protection Profile PP-0084, but also for integrated secure elements in accordance with the latest profiles required by the German BSI, such as PP-0117. These protection profiles map out very comprehensive threat and security models, and our secure element is designed so that its implemented security mechanisms address the risks described there. For all requirements, we also ensure clear traceability back to the underlying model. Our first chip already addresses a wide range of these issues and will be successively expanded in future iterations.
Andreas Seelos-Zankl: Our secure element is based on Common Criteria, with a target protection level of EAL4+ and the protection profiles mentioned earlier. It is protected against both remote attacks via compromised host systems and local, physical attacks. We rely on a small, clearly defined Trusted Computing Base with strictly limited interfaces, as well as mechanisms such as Secure Boot and Secure Update. Encryption of memory and data transfers, side-channel hardening, and redundant execution for error detection, for example, protect against local attacks. In addition, dedicated hardware components and, starting with the next version, sensors as well, monitor the chip and can trigger an incident response when an attack is detected, such as deleting keys or permanently disabling the system.
Which cryptographic methods are supported and how do you ensure that the de-sign remains cryptographically future-proof in the long term?
Andreas Seelos-Zankl: When it comes to cryptography, we rely on algorithms from the field of post-quantum cryptography. Our chip is based on the standards and recommendations by BSI and NIST; in the first version of the secure element, we support algorithms selected in the NIST process: ML-DSA (CRYSTALS-Dilithium), ML-KEM (CRYSTALS-Kyber), and SLH-DSA (SPHINCS+); the next version will add FN-DSA (Falcon) and FrodoKEM. This means we support a wide range of PQC algorithms compared to other secure elements. The challenge lies in efficiently implementing all of them on relatively low-performance hardware, a microcontroller with a target frequency of approximately 100 MHz. Through targeted hardware acceleration, we manage to ensure that operations such as key generation and signature calculation take less than ten milliseconds, which is sufficient for many applications. We have also placed great emphasis on crypto-agility: Currently, the hybrid use of established cryptographic schemes together with PQC schemes is recommended. Accordingly, we support the combination of, for example, RSA or elliptic curves with post-quantum algorithms, ensuring that our secure element is cryptographically future-proof, modern, and suitable for many application scenarios.
What interfaces can be used to connect the secure element, and how complex is it typically to migrate an existing solution to it?
Augusto Wankler Hoppe: We have developed our own internal, secure boot and communication interface that handles communication with the rest of the SoC – that is, the chip into which our secure element can be integrated. It is based on the Caliptra Core standard. In addition, we also use this standardized interface for provisioning and other commissioning activities. Externally, the secure element features a standardized SPI interface through which it connects to the rest of the system. Additionally, there are dedicated LC/JTAG connections for programming eFuses – that is, permanent chip settings – and for lifecycle provisioning, which involves the gradual, secure configuration of a chip throughout its lifecycle. Our secure element can be used both as an integrated component in a SoC and as a discrete component.
Andreas Seelos-Zankl: The integration effort is comparable to switching to a different microcontroller system. We operate within the standard market framework and support common interfaces.
What specific tools do you provide companies to help them integrate the secure element without requiring them to be experts in hardware security themselves? What resources do you make available for this purpose?
Augusto Wankler Hoppe: We offer custom chip development and handle the entire development process. We support our customers from requirements analysis and specification through design and verification to physical implementation, commissioning, testing, and validation. In addition, we offer our customers so-called turnkey solutions. Specifically, this means we handle the entire hardware development process: from RTL design through verification and tape-out to silicon validation and low-level software components. Together with Fraunhofer AISEC, we provide everything a customer needs, without requiring them to possess in-depth technical expertise or maintain their own security experts. This end-to-end capability is rare in the European research landscape and enables us to provide customers not just with IP, but with a solution that can be integrated immediately and is ready for use.
Which customers are you primarily targeting with the secure element?
Andreas Seelos-Zankl: With our secure element, we specifically target small and medium-sized enterprises by enabling a high level of security even in smaller quantities and by reducing international dependencies through regional development and manufacturing. Stable supply chains and the ability to adapt the system to specific requirements are key here. While established standards such as TPM and Caliptra exist, they often only partially meet customer needs. This is where we step in by developing additional functions to bridge the gap. We consistently find this adaptability to be a central requirement in our discussions with customers. To this end, we offer a comprehensive service catalog, including security testing and validation in realistic target environments, such as for industrial or automotive control units. This allows us to provide not only functional flexibility but also flexible, application-specific validation. This includes the kind of verification required, for example, by the CRA, where independent testing is mandated.
Augusto Wankler Hoppe: We have the capability to implement and deliver this technology as a chip. This is ultimately what makes it accessible to startups and SMEs in the first place. That’s exactly where our focus lies: We want to support customers who previously had no access to secure chip technology, whether due to cost or complexity. We position ourselves as a close development partner: We talk to the customer, understand their system requirements, and jointly develop a tailor-made solution, from specification to silicon validation. At the same time, we also cater to larger design houses seeking an integrated, open-source secure element for their own SoC platforms.
What technical or regulatory developments are shaping your roadmap, and what features are you planning next?
Augusto Wankler Hoppe: Together, we are driving the technological advancement of the secure element. Specifically, our roadmap calls for integrating our secure element into larger, chiplet-based systems in the future. In these architectures, it serves as a Root of Trust for the entire chiplet system and as the starting point for system deployment, particularly for provisioning and secure system boot. At the same time, we are pursuing a roadmap for the development of the secure element itself: Among other things, we plan to integrate additional sensors to further enhance protection against physical tampering and manipulation. As Andreas already mentioned, we have developed and documented several threat models; however, the full implementation of all measures will take time. In the long term, this will make our chip even more resilient, for example, against specific side-channel attacks. In these attacks, conclusions about secret data are drawn from power consumption or execution times. We take this robustness into account both during the design stage using models (pre-silicon phase) and later during testing of the finished chip in post-silicon laboratory analysis. In the future, we will also make these enhanced protection mechanisms available to customers as part of integration into their systems.
Andreas Seelos-Zankl: In the future, the secure element will be available as a standalone chip, as a SoC component, and as a chiplet. From a security perspective, we are further expanding the active protection measures and implementing them even more thoroughly in the GlobalFoundries 22-nanometer process. Due to the characteristics of the manufacturing technology, this task presents a new challenge for every process. For cryptography, we are planning additional protection mechanisms, particularly side-channel and error protection for post-quantum algorithms. This is a field in which the OpenTitan project itself is also involved and to which we are equally committed. At the same time, we are considering support for additional cryptographic algorithms to further strengthen the broad adoption of our secure element. In the long term, security certification is also a clear goal: We aim to develop a chip version that, similar to today’s highly secure systems, overcomes relevant certification hurdles, even though we do not intend to target the high-end segment; the timeframe for this is at least five years.
Autoren

Andreas Seelos-Zankl
Andreas Seelos-Zankl is a Principal Scientist at Fraunhofer AISEC in the “Hardware Security, Secure Circuits and Systems” department. He earned his master’s degree in Information and Computer Engineering from Graz University of Technology, specializing in information security. He completed research stays in the USA and Singapore. He has been working at Fraunhofer AISEC for twelve years. His research focuses on post-quantum cryptography, RISC-V and open-source hardware, microarchitectures, and side-channel attacks.
Contact: andreas.zankl@aisec.fraunhofer.de
Augusto Wankler Hoppe
Augusto Hoppe is Technical Lead at Fraunhofer IIS in the “Integrated Digital Systems” department. In 2021, he completed his joint Ph.D. on hardware-based techniques for control-flow protection and processor fault tolerance at KIT and UFRGS (Brazil). Since then, he has been leading the tape-out of the Fraunhofer secure element. His research and work focus on security system architecture, secure hardware development, Root of Trust, RISC-V-based SoCs, and open-source projects.
Contact: augusto.hoppe@iis.fraunhofer.de